
External Surface
What your organization actually exposes on the Internet.
NATIVE EASM · VULNERABILITY INTELLIGENCE · THREAT INTELLIGENCE
Act on what matters first.
YellowShielder maps your exposed surface, connects vulnerabilities to real threats and turns scattered signals into evidence-backed action priorities.
One authorized domain is enough to start · First prioritized reading of your exposure
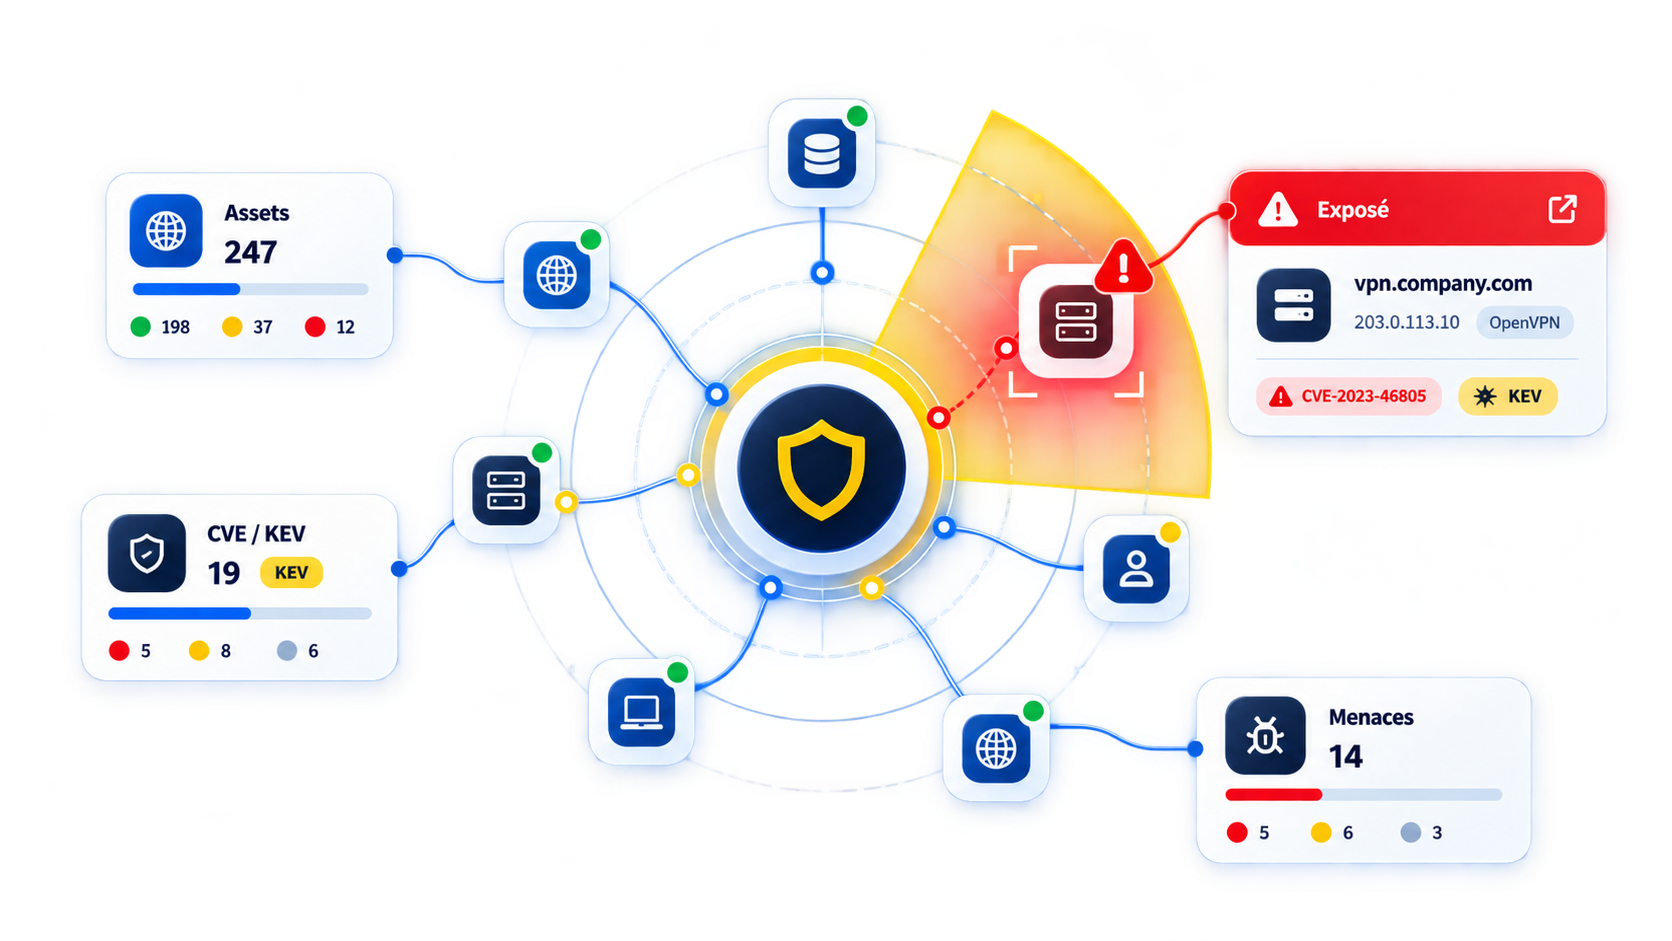
THREAT-INFORMED VULNERABILITY OPERATIONS
The risk is not the CVE alone. It is the exploitable path to your organization, put back into context and backed by evidence.
01 · EXTERNAL ATTACK SURFACE
YellowShielder observes your perimeter from the outside, discovers reachable assets and tracks how they change over time.
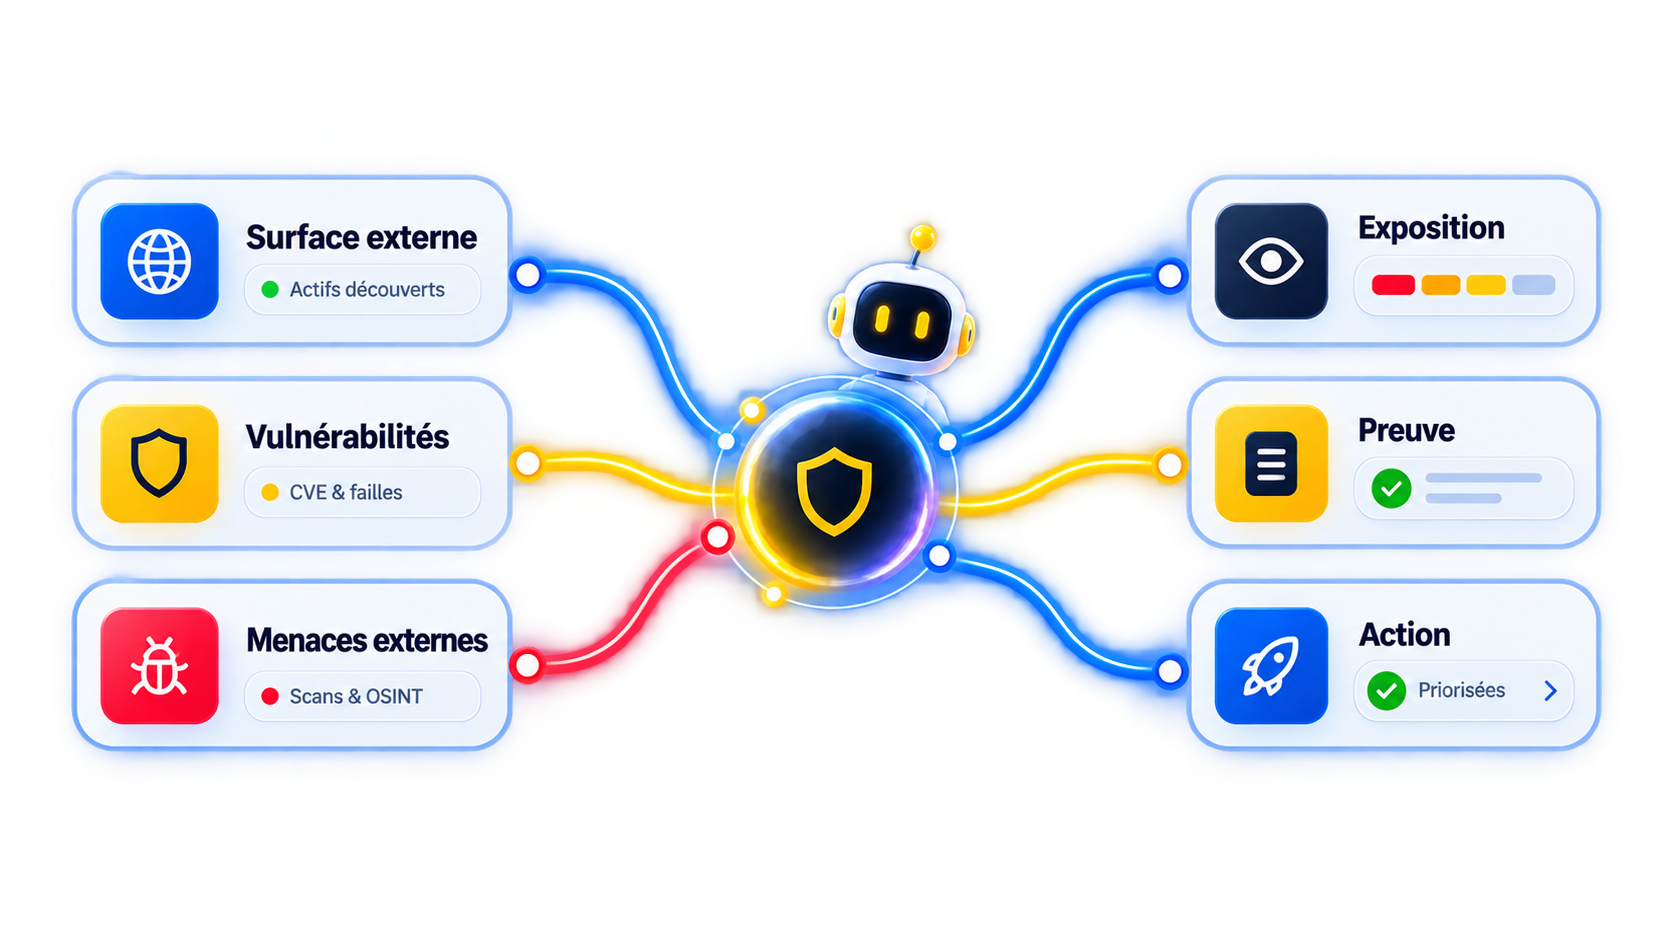
02 · EXPOSURE LENS
The Exposure Lens brings external surface, vulnerabilities and threats together. It produces an operational reading: exposure, evidence and next action.
Surface + exploitability + threat → actionable exposure
THREE SOURCES OF CONTEXT
Each signal keeps its evidence, but takes its value when connected to the others on the same asset.
What your organization actually exposes on the Internet.
What can be attacked according to the CVE, KEV, PoCs and known exploitation.
What the adversary already knows: leaks, identities and external activity.
What has been observed, where, when and why it matters.
The criticality and ownership that steer the next action.
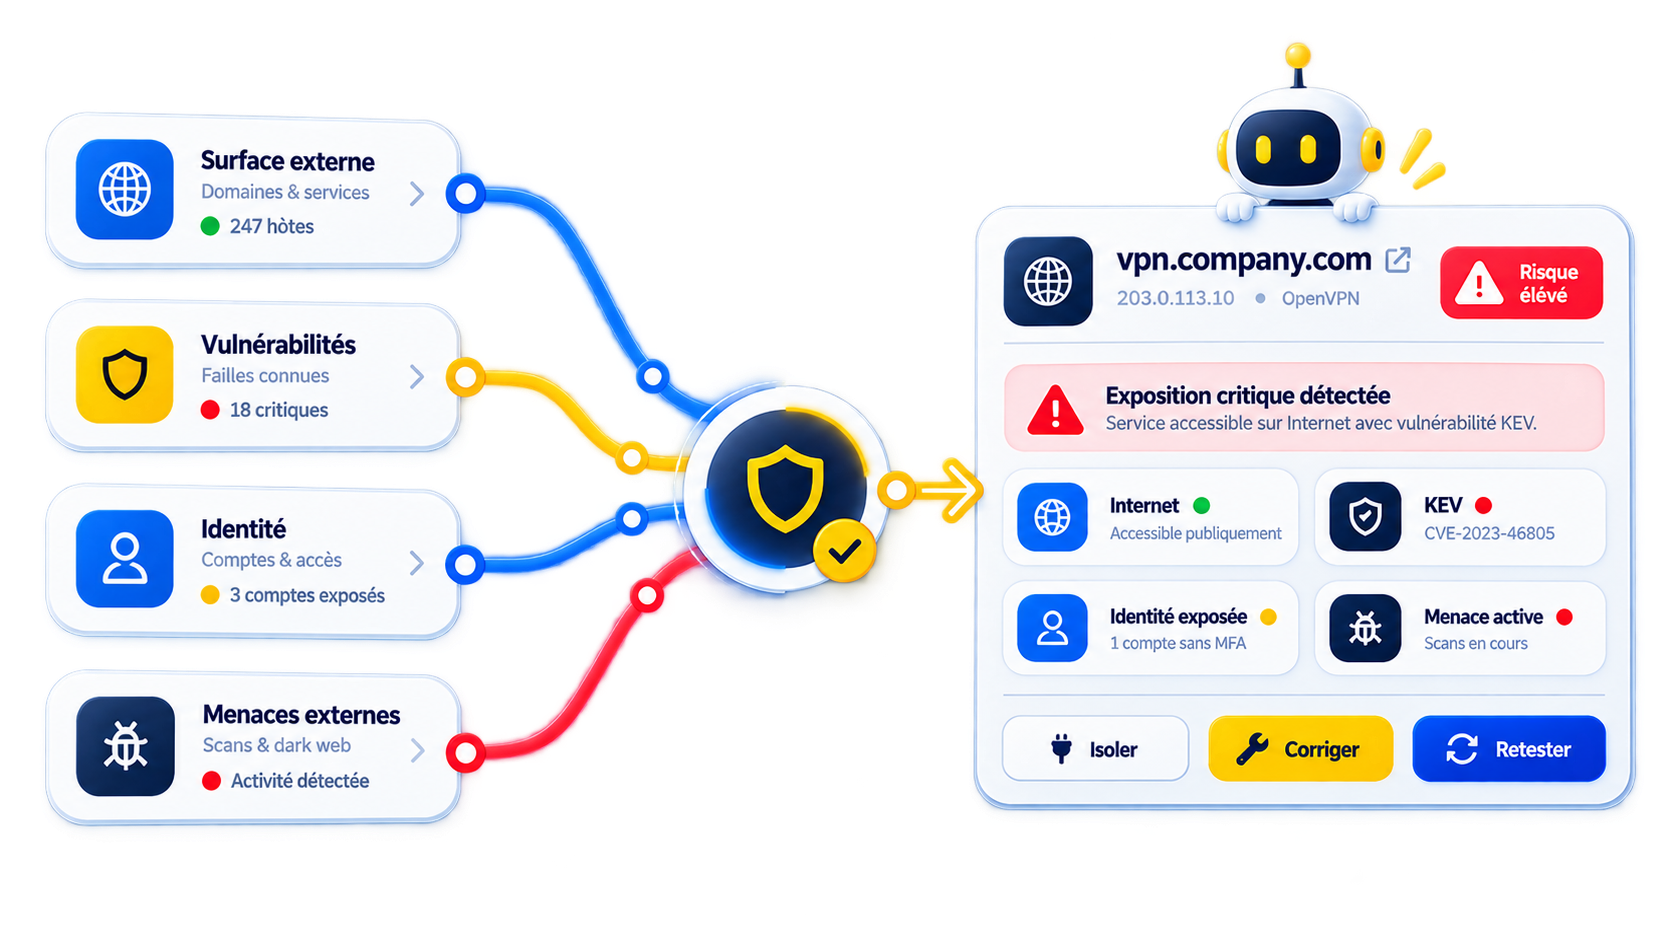
03 · EXPOSURE CONTEXT ENGINE
YellowShielder gathers the signals concerning the same asset and explains why the exposure must be addressed now.
Discover → verify → enrich → correlate → act
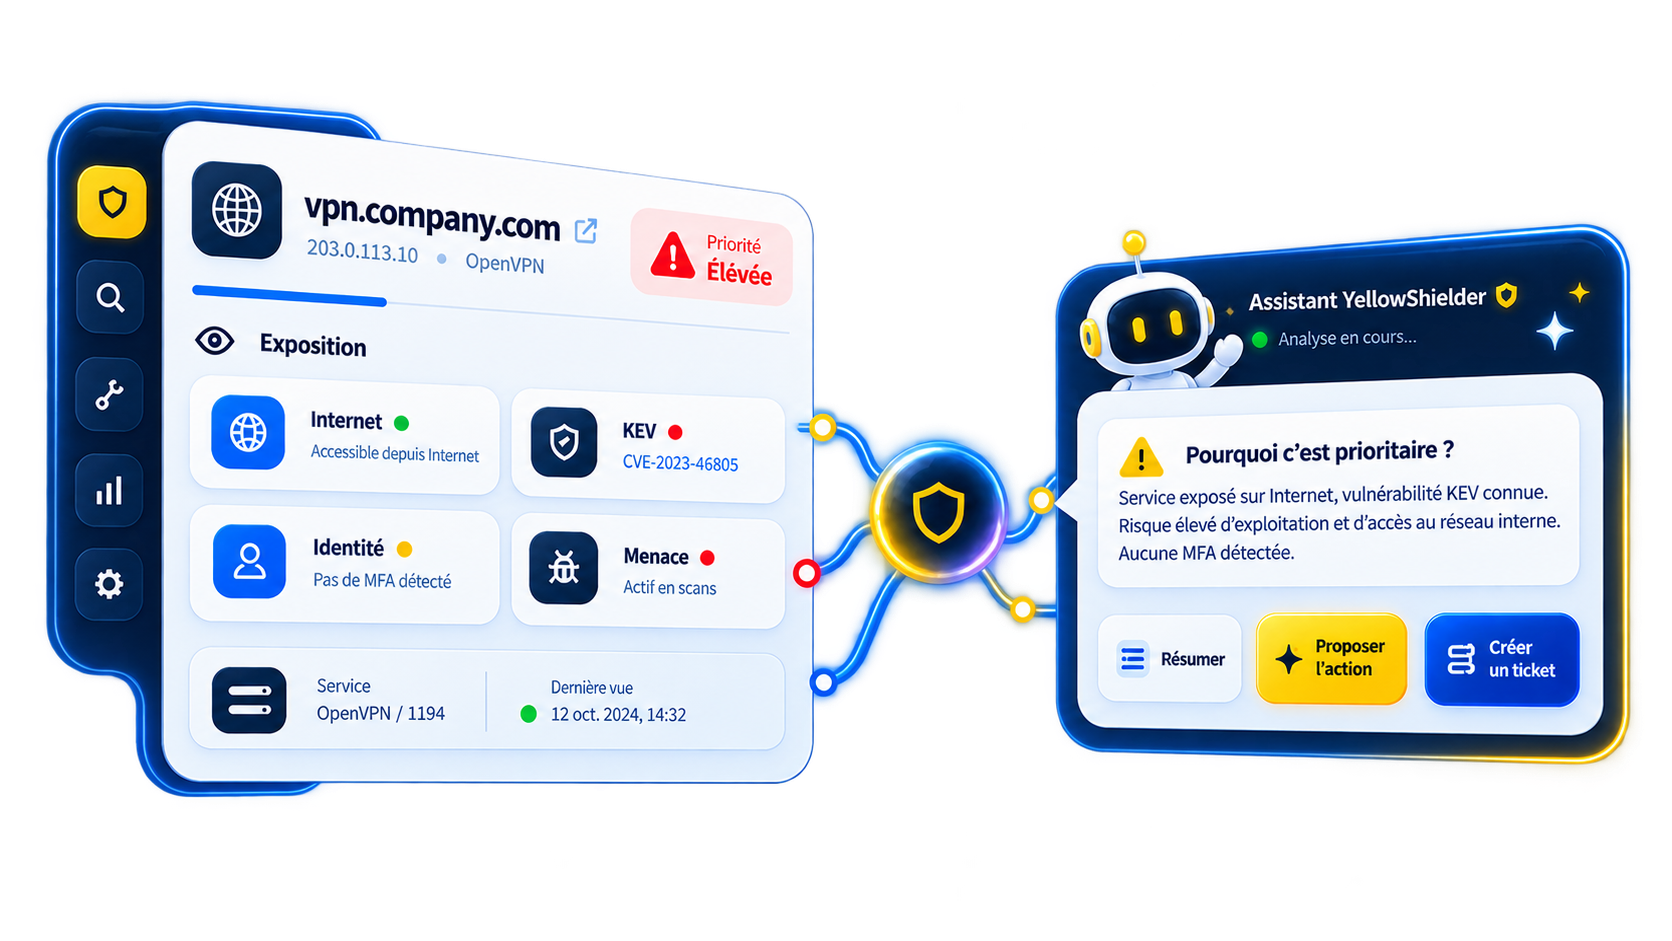
04 · AI-ASSISTED INVESTIGATION
The assistant accelerates the investigation from the context actually observed. It summarizes evidence, explains urgency factors and prepares the next action without hiding the reasoning.
AI assists. Evidence remains accessible.
One shared discovery, context and evidence foundation serves several operational security objectives.
Get a first reading of what an attacker can discover from an authorized corporate domain.
GainA clear starting point and first prioritized investigations.
Get my Exposure SnapshotTrack new assets, exposed services and significant changes between scans.
GainMove from a one-off audit to continuous vigilance.
Book a demoPut CVEs and CVSS back into the context of the asset, KEV, PoCs and observed exploitation.
GainFocus remediation on the paths that are actually exploitable.
Book a demoConnect credentials, emails and leak signals to the assets and access concerned.
GainIdentify exposures combining a technical weakness with identity risk.
Book a demoBring evidence, explanation, owner and next action together around the same exposure.
GainCut the manual correlation before action and retest.
Book a demoKeep dated observations, priority factors and treatment history.
GainReuse the same evidence for operations, management and audits.
Book a demoSECURITY, INTEGRATIONS AND TRUST
The perimeter, authorizations, identities, flows and connectors are defined with your teams depending on the context enabled.
Scans target only explicitly authorized perimeters.
Roles, MFA, logging and tenant isolation depending on the configuration.
SIEM, ITSM, Threat Intelligence, messaging and webhooks depending on available connectors.
History and views that can support ISO 27001, NIST CSF, DORA and GDPR depending on the context.
Not necessarily. YellowShielder adds an outside-in view and a correlation layer between assets, vulnerabilities, external signals and evidence. It can complement the scanners, SIEM, ITSM tools and Threat Intelligence sources already in place.
A finding is an isolated observation, such as an open port, a CVE or an exposed identifier. An exposure connects several observations to the same asset and explains why they form an operational situation to address.
No. CVSS remains useful, but the platform can also consider Internet exposure, CISA KEV, PoCs, observed exploitation, identity signals, threat context and available evidence.
No. The assistant accelerates understanding and the preparation of the action. Priority factors and evidence stay accessible so the security team keeps control of the decision.
A corporate domain and an explicitly authorized perimeter are enough to start a demo or request an External Exposure Snapshot.
EXTERNAL EXPOSURE SNAPSHOT
Give us an authorized corporate domain and get a first prioritized reading of your external exposure.
Authorized perimeter · Contextualized reading · Conversation with a Cyber expert